Software teams face growing pressure to release applications quickly while protecting sensitive information, infrastructure, and customer data. When security checks happen only at the end of development, businesses may discover problems late in the delivery process. DevSecOps Consulting Services in Pune help organizations introduce security practices across development, testing, deployment, and operations. Goognu works with businesses to understand their existing software delivery environment and identify ways to incorporate security into everyday workflows. Our consulting approach focuses on practical improvements that support development teams, strengthen security processes, and help organizations manage application delivery with greater visibility.
Security requirements can vary depending on the application, technology stack, business sector, and infrastructure being used. A company developing a cloud-based product may face different concerns from an organization managing internal enterprise applications. DevSecOps Consulting Services help businesses evaluate these differences and plan security processes around their technical needs. Goognu supports organizations in reviewing their development workflows, identifying security gaps, and considering suitable testing and monitoring practices. Our approach brings development, security, and operations requirements into the same discussion, helping teams create a more organized process for identifying and addressing security concerns throughout the software lifecycle.
Pune has a growing technology environment that includes software development companies, product businesses, IT service providers, and organizations building digital applications. As businesses expand their software operations, they may need better coordination between development speed and security requirements. DevSecOps Consulting solutions in Pune help organizations explore methods for introducing security into existing development processes. Goognu works with businesses to understand their current tools, application architecture, and delivery practices. Based on these requirements, we help teams consider suitable approaches for security testing, workflow integration, access management, and operational oversight without treating security as a separate final-stage activity.
A secure software delivery process requires attention throughout the application lifecycle. Code changes, third-party dependencies, infrastructure configurations, and deployment activities can all introduce potential risks. Businesses need suitable methods to identify issues and establish processes for addressing them. Goognu provides DevSecOps Consulting Services in Pune to support organizations in reviewing their security and delivery requirements. Our consulting services focus on integrating security considerations into development and operations workflows. Businesses that need broader development and operational support can also explore DevOps Consulting Services in Pune as part of their technology improvement plans.
Software development involves frequent code changes, multiple environments, and collaboration between different technical teams. When security is handled separately from these activities, issues may be identified late or require additional work before an application can be released. DevSecOps introduces security considerations into the development and delivery process, helping teams review risks earlier in the workflow.
Goognu's DevSecOps Consulting Services in Pune help businesses examine their existing software delivery methods and identify opportunities to incorporate security practices. The consulting approach considers the organization's application requirements, development processes, and infrastructure environment.
Security checks can be included at different stages of software development. The appropriate methods depend on the application and the types of risks the business needs to manage.
Goognu helps organizations consider processes such as:
Improving Coordination Between Teams
Development, security, and operations teams may have different responsibilities and priorities. A shared workflow can help establish clearer communication about security findings, remediation activities, and release requirements.
Goognu supports businesses in reviewing how these teams work together and identifying ways to improve coordination. This approach helps organizations consider security as part of their regular software delivery activities rather than relying only on final-stage checks.
A DevSecOps strategy needs to address more than application code. Security considerations can also involve infrastructure configurations, access permissions, build environments, and deployment processes. Businesses benefit from reviewing the different areas that may influence the security of their software delivery environment.
Through DevSecOps Consulting solutions in Pune, Goognu helps organizations understand these considerations and plan workflows that suit their technology environment. Our consulting approach focuses on identifying relevant security activities and connecting them with existing development and operational processes.
Different parts of a software environment may require different security checks and management practices. Reviewing these areas helps teams understand where security controls can be introduced.
Businesses may consider:
Integrating Security into Delivery Pipelines
A delivery pipeline can include automated activities for building, testing, and deploying software. Security checks may be introduced at relevant points based on the application's requirements.
Goognu helps organizations review their pipeline structure and consider suitable integration methods. The focus is on planning security activities that support the development process while ensuring findings are reviewed and addressed through appropriate procedures.
Every organization has different application architectures, development practices, security requirements, and infrastructure arrangements. A consulting approach should consider these differences before suggesting changes to existing workflows. Businesses may require support with application security, cloud environments, automated pipelines, or the coordination of security responsibilities across teams.
Goognu provides DevSecOps Consulting Services in Pune to help organizations review their current software delivery practices and understand possible improvements. Our approach focuses on the specific requirements of each business and the technical environment in which its applications operate.
Understanding the existing development and operations setup is an important part of planning DevSecOps improvements. It helps businesses identify relevant security needs and consider how they can be incorporated into established processes.
Goognu supports organizations with:
Supporting Continuous Security Improvements
Security management is an ongoing activity because applications, dependencies, infrastructure, and potential risks can change over time. Businesses may need to review their processes regularly and update their security practices when requirements evolve.
Goognu helps organizations consider how security activities can be maintained across the software lifecycle. Companies that also require support with development workflows and operational processes can explore DevOps Consulting Services in Pune for related consulting requirements.
Our focus is on helping businesses establish a clearer direction for their DevSecOps practices based on their application needs, security priorities, and existing technology environment.
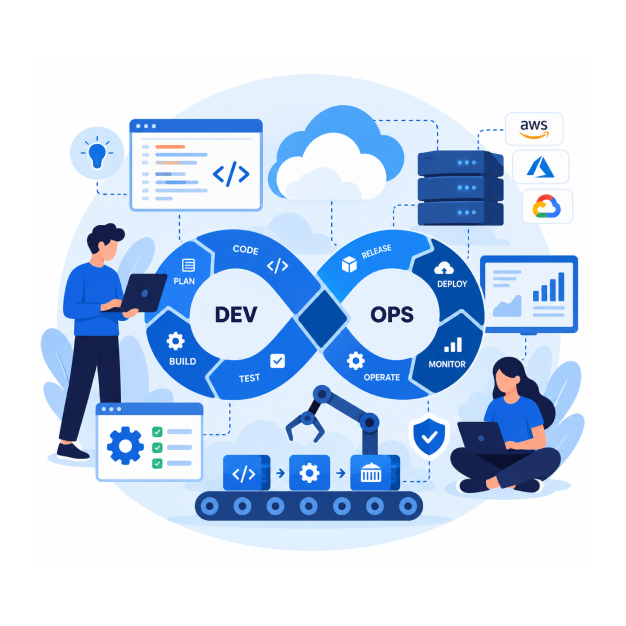
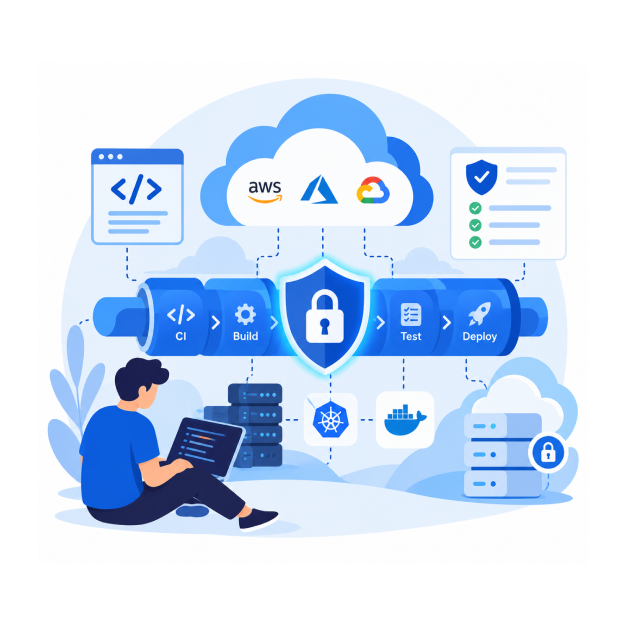

Plan security activities across development, testing, deployment, and operations to support consistent software delivery practices.
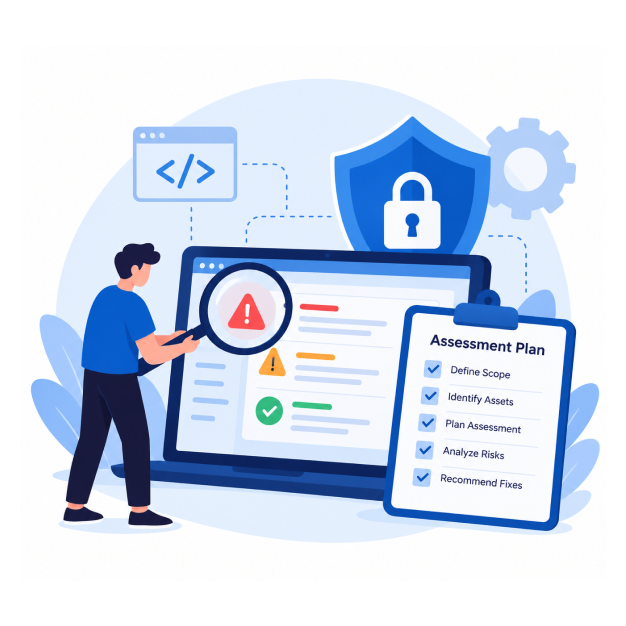
Review code, dependencies, and application components to identify potential areas requiring security attention.
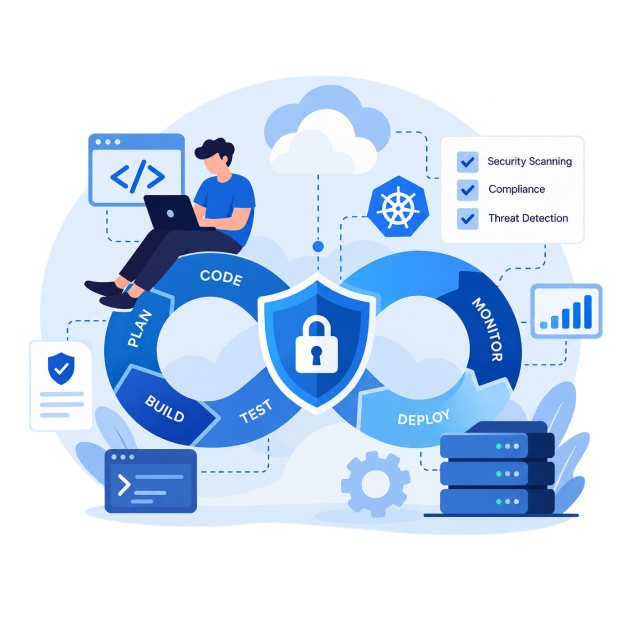
Consider security testing and validation within CI/CD workflows based on application and deployment requirements.
Review access controls, configurations, and deployment environments to support better security management across technical systems.
Goognu provides Devsecops Consulting Services since a very long time and has more than 13 years of experience in the industry.
Take advantage of Goognu's Devsecops Consulting Services that provide greater security and help organizations work more efficiently and keep organizations' data secure.

Goognu provides Devsecops Consulting Services since a very long time and has more than 13 years of experience in the industry.
goognu offers round-the-clock support; ensure you are never alone and always assisted; we're here to help. Reliable 24/7 services for your business needs.


Goognu's AWS Consulting Services helped us migrate our entire infrastructure to the AWS cloud. Their team of experienced cloud engineers provided us with an architecture that met our requirements and provided us with the necessary support to ensure an absolute migration.


We have partnered with Goognu Data Services Pvt. Ltd. to help us move our data to the cloud. The team was very helpful in understanding our needs and developing a plan to make the transition as smooth as possible. Now we are able to access our data quickly and securely from anywhere.

We recently engaged with Goognu to move our entire IT framework to the cloud. The team was professional and knowledgeable, and provided us with the expertise we needed to make the transition quickly and efficiently.

Working with Goognu has been a wonderful experience. They took the time to understand our business and the specific needs of our project. They gave us excellent advice that helped us make informed decisions about our cloud infrastructure.

You will explore the services provided by Goognu in various cities across the world.



 India

 Canada
 United Kingdom
 New Zealand
 USA
 UAE
 SGP
 Australia
 CALL
NOW


Let’s connect
We are here to assist you with any questions or concerns you may have regarding our AWS consulting services. Please let us know if you need assistance, our team of experienced professionals is here to answer your questions and help you find the best solution. Thank you for choosing Goognu.
Schedule a call
location_on Unit No.538, JMD Megapolis, Sohna Road, Gurugram-122018.
mail hello@goognu.com
call +91 9971018978