Most security problems in software delivery do not come from a single bad decision. They come from security being treated as a final checkpoint instead of something built into the process from the beginning. Our DevSecOps Consulting Services in Gurgaon are focused on changing that. We work with your engineering team to identify where security gaps typically show up in your current pipeline and help build a process where security checks happen alongside development, not after it.
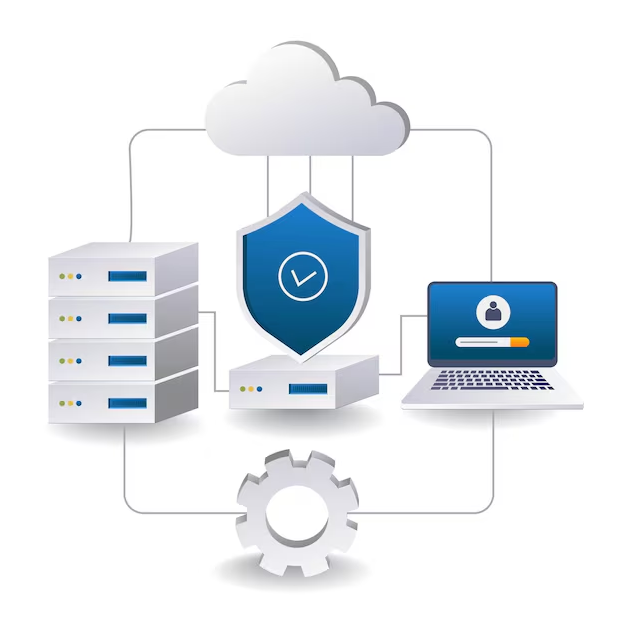
We start by looking closely at how your team currently builds, tests, and deploys software. This means reviewing your existing pipeline, the tools already in use, how code gets reviewed, and where security testing currently fits, if it fits at all. From there, we put together recommendations that are specific to your setup, covering things like automated security scanning, dependency checks, access controls, and secrets management within your CI/CD workflow.
Security practices need to keep pace with how fast your team ships code. A process that works for a small team pushing weekly releases will not hold up for a team deploying multiple times a day. Our consulting work accounts for this from the start, and we stay involved during implementation to make sure the recommendations actually work in practice, not just on paper.
If you are comparing DevSecOps Consulting Services and looking for DevSecOps Consulting solutions in Gurgaon, it is worth checking whether a provider actually reviews your existing pipeline before recommending tools. We spend real time understanding your current setup first, because security recommendations that ignore how your team actually works tend to get ignored too. Many of our clients also work with our DevOps Consulting Services in Gurgaon team separately, since strengthening the underlying delivery process often makes security improvements easier to implement as well.
Security gaps tend to hide in places teams are not actively looking. A dependency that has not been updated in months, a secret sitting in a config file, or a deployment step with broader access permissions than it actually needs. Individually these might seem minor, but they add up to real risk over time.
Areas we typically review during a DevSecOps assessment:
We do not push the same checklist onto every client. A fintech company handling sensitive customer data has very different compliance pressures than a smaller product team shipping an internal tool. Our review takes into account your industry, your existing tech stack, and the size of your engineering team before recommending anything.
For teams that already have some security tooling in place but are not confident it is actually catching issues, this kind of outside review often finds blind spots that internal teams have gotten used to overlooking. For teams starting with very little security automation, we help introduce checks gradually so they do not slow the team down more than necessary.
The goal is not to add a separate security process that runs parallel to development. It is to fold security checks into the pipeline your team already uses, so they happen automatically instead of depending on someone remembering to run them manually.
What this usually involves:
We try to avoid recommendations that create friction without a clear payoff. Adding five new tools that nobody ends up using does not improve security, it just adds noise. Instead, we prioritize changes based on actual risk and work through implementation with your team so the new checks become part of the normal workflow rather than an extra burden.
Where possible, we also try to reduce false positives in automated scanning, since teams tend to start ignoring security alerts altogether once they get too noisy to be useful.
Security is not something you fix once and move on from. New vulnerabilities get discovered, dependencies need updating, and your infrastructure keeps changing as your product grows. A consulting engagement can set the right foundation, but maintaining that foundation is ongoing work.
What typically continues after the initial consulting phase:
Some teams prefer to take everything forward on their own once the consulting engagement is complete, and we make sure the handover includes everything needed for that. Others want continued support without expanding their internal security or DevOps headcount. For teams looking to strengthen the broader delivery pipeline alongside security, our DevOps Consulting Services in Gurgaon team can work on the operational side in parallel.
Keeping these as separate but connected services means businesses can choose the level of support that actually fits their situation, whether that is a focused security review or an ongoing partnership covering both delivery and security together.

We closely examine your current development and deployment process before suggesting any security changes, keeping every recommendation grounded in h…
Security fixes get ranked by real risk and impact, helping your team fix the most important gaps first instead of chasing every possible issue.
We stay involved as security checks get built into your pipeline, so your team never has to figure out execution alone.
As your release frequency and team size increase, we adjust your DevSecOps Consulting Services so they keep pace instead of slowing you down.
Goognu provides Devsecops Consulting Services since a very long time and has more than 13 years of experience in the industry.
Take advantage of Goognu's Devsecops Consulting Services that provide greater security and help organizations work more efficiently and keep organizations' data secure.

Goognu provides Devsecops Consulting Services since a very long time and has more than 13 years of experience in the industry.
goognu offers round-the-clock support; ensure you are never alone and always assisted; we're here to help. Reliable 24/7 services for your business needs.


Goognu's AWS Consulting Services helped us migrate our entire infrastructure to the AWS cloud. Their team of experienced cloud engineers provided us with an architecture that met our requirements and provided us with the necessary support to ensure an absolute migration.


We have partnered with Goognu Data Services Pvt. Ltd. to help us move our data to the cloud. The team was very helpful in understanding our needs and developing a plan to make the transition as smooth as possible. Now we are able to access our data quickly and securely from anywhere.

We recently engaged with Goognu to move our entire IT framework to the cloud. The team was professional and knowledgeable, and provided us with the expertise we needed to make the transition quickly and efficiently.

Working with Goognu has been a wonderful experience. They took the time to understand our business and the specific needs of our project. They gave us excellent advice that helped us make informed decisions about our cloud infrastructure.

You will explore the services provided by Goognu in various cities across the world.



 India

 Canada
 United Kingdom
 New Zealand
 USA
 UAE
 SGP
 Australia
 CALL
NOW


Let’s connect
We are here to assist you with any questions or concerns you may have regarding our AWS consulting services. Please let us know if you need assistance, our team of experienced professionals is here to answer your questions and help you find the best solution. Thank you for choosing Goognu.
Schedule a call
location_on Unit No.538, JMD Megapolis, Sohna Road, Gurugram-122018.
mail hello@goognu.com
call +91 9971018978