Artificial intelligence is moving from experimental projects to important business operations. Companies now use AI to support customer service, hiring, fraud detection, software development, marketing, data analysis, and many other areas. As AI becomes more involved in daily decisions, businesses also need to answer an important question: how can they make sure AI is being used safely and responsibly?
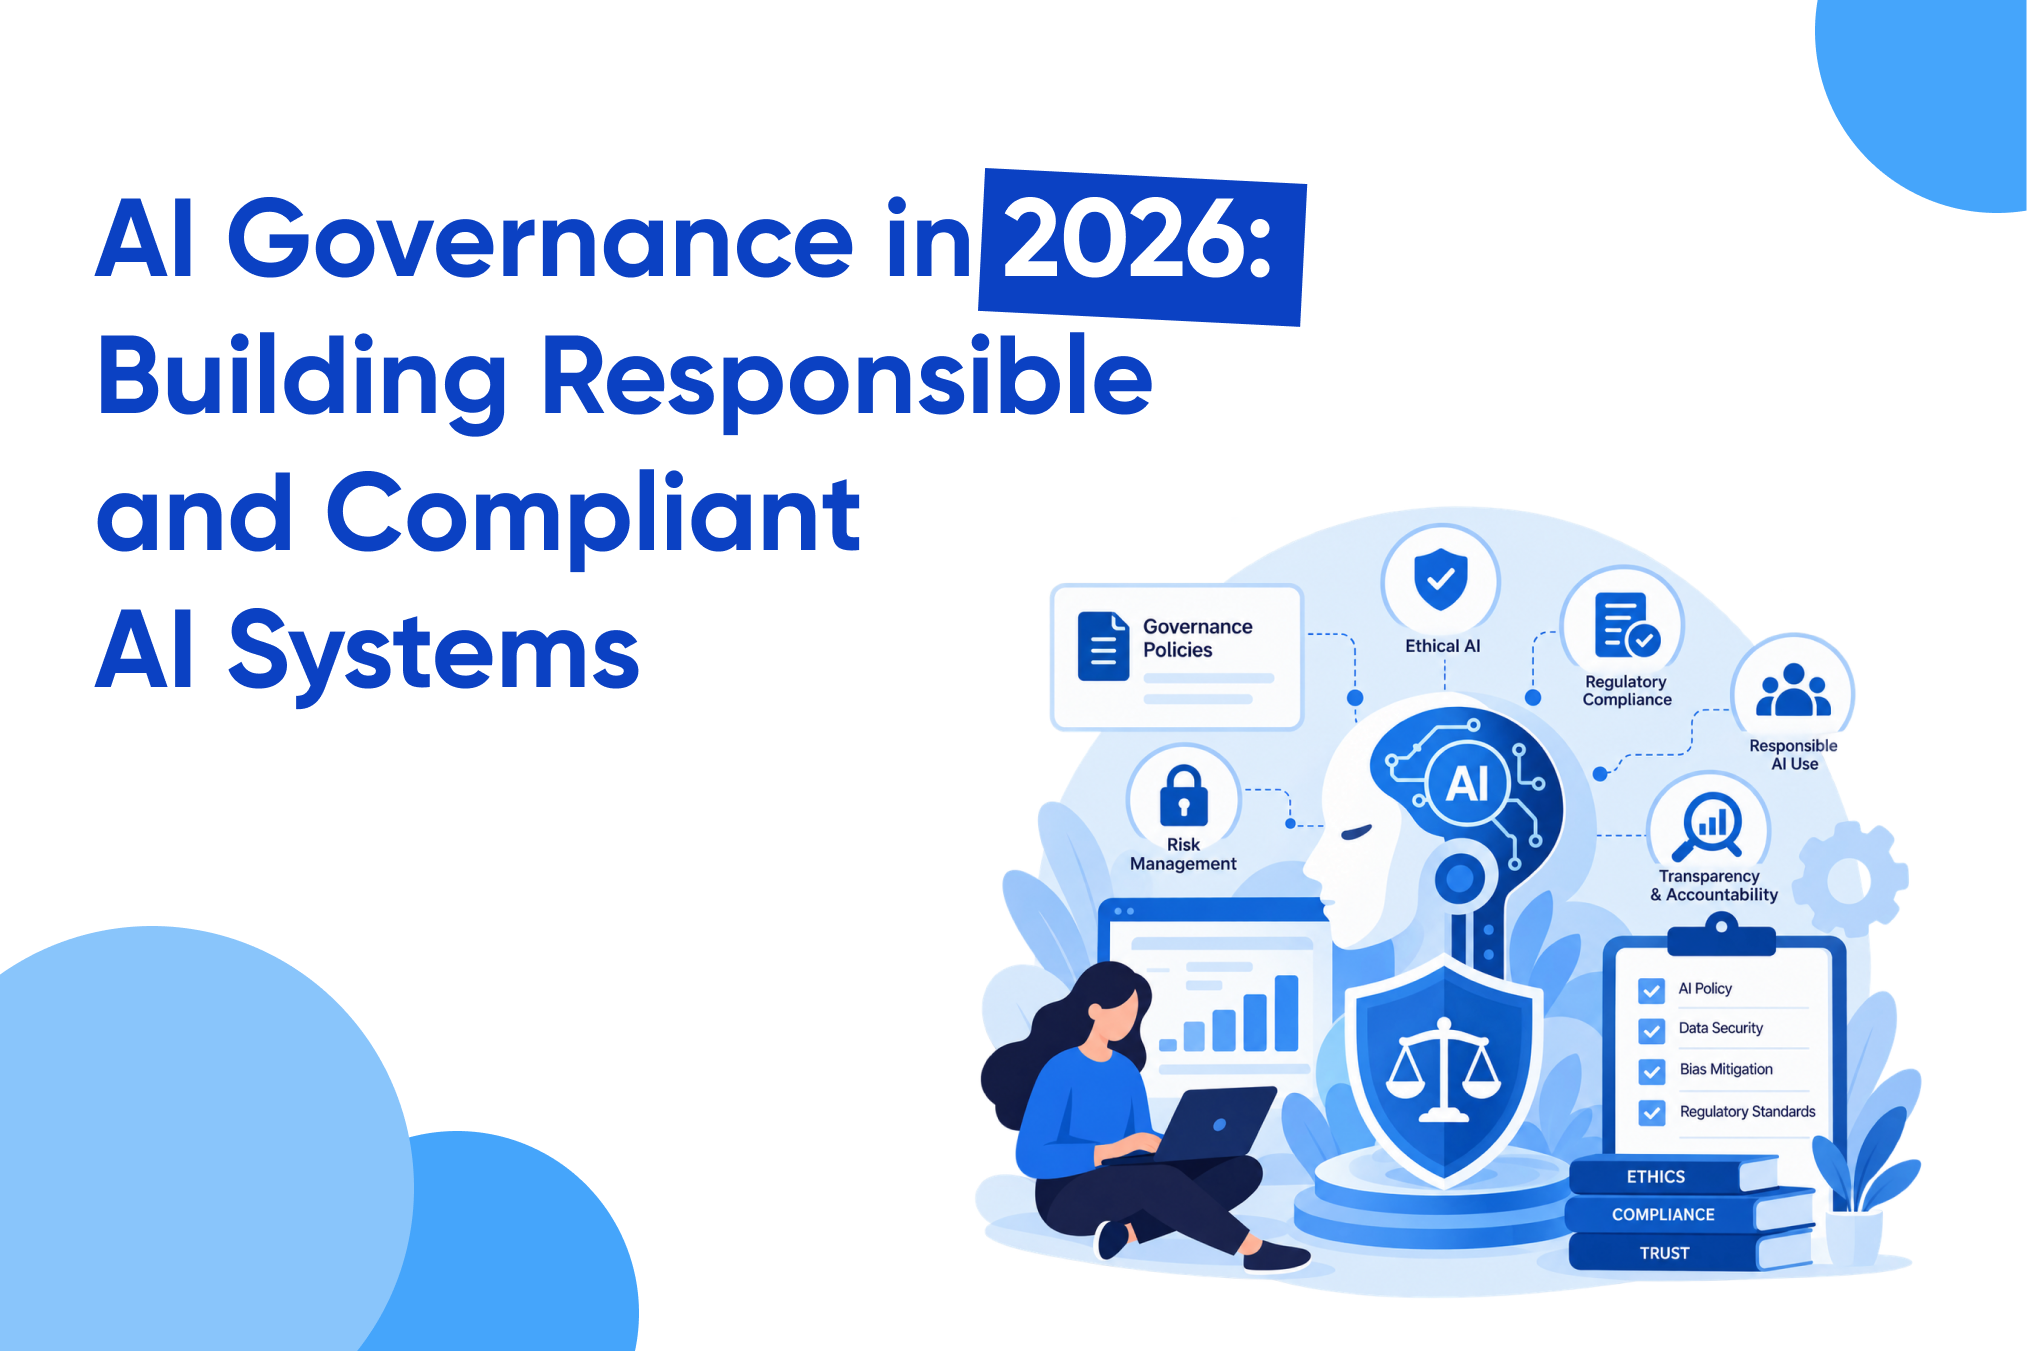
This is where AI Governance becomes important. It gives businesses a structured way to manage how AI systems are developed, deployed, monitored, and improved. In 2026, governance is becoming less about having a set of rules on paper and more about making responsible AI practices part of everyday technology decisions.
AI Governance refers to the policies, processes, roles, and controls used to manage AI throughout its lifecycle. It covers everything from choosing training data and developing models to monitoring their performance after deployment.
A good governance approach helps answer practical questions:
These questions become more important as AI systems influence decisions that affect customers, employees, and business operations.
AI adoption is growing, but so are concerns around privacy, security, fairness, transparency, and accountability. A system may produce useful results while still creating risks if its data is poor, its decisions cannot be explained, or its outputs are used without proper human review.
Organizations therefore need governance before problems appear rather than after an incident occurs.
Strong governance can help businesses:
The goal is not to slow AI adoption. It is to create conditions where businesses can use AI with greater confidence.
An AI governance framework should be practical enough to support real projects. A complicated policy that nobody follows will not provide much protection.
A useful framework normally begins by identifying every AI system being used across the organization. Businesses should know what each system does, what information it processes, who owns it, and what level of risk it may create.
The framework can then define rules for:
AI development:
Teams should follow clear standards when selecting data, building models, testing outputs, and preparing systems for deployment.
Access and responsibility:
Organizations need defined roles for developers, business teams, security professionals, legal teams, and decision-makers.
Testing and review:
AI systems should be tested for accuracy, security, bias, reliability, and other risks before they are widely used.
Ongoing monitoring:
Governance should continue after deployment because model performance and usage can change over time.
Documentation:
Important information about models, data sources, testing, decisions, and changes should be properly recorded.
Many organizations focus heavily on testing before launching an AI system. However, risks can appear after deployment as users interact with the system in unexpected ways.
This makes AI risk management an ongoing process.
Businesses should monitor areas such as unusual model behavior, inaccurate outputs, data exposure, security threats, changes in performance, and inappropriate use. Higher-risk systems may also need stronger controls and more frequent reviews.
Risk levels should not be the same for every AI application. An AI tool that summarizes internal documents may create different risks from a system used to make decisions about employment, financial services, healthcare, or access to important services.
A risk-based approach allows organizations to give greater attention to systems where mistakes could have more serious consequences.
The idea of responsible AI goes beyond simply making an AI system accurate. Businesses also need to consider how the system affects people.
Human oversight is especially important when AI outputs influence significant decisions. Employees should understand when they are working with AI and when they need to question or review its recommendations.
For example, an AI system can help identify suitable candidates during recruitment, but organizations may still need human review before making a hiring decision. Similarly, AI can flag unusual financial activity, while trained professionals can investigate the case before taking action.
Human oversight creates an important balance between automation and accountability.
Regulations and industry expectations around artificial intelligence continue to develop. Organizations operating across different countries may also need to consider different legal requirements.
AI compliance therefore needs to be part of the AI lifecycle rather than a final check before launch.
Businesses should understand which rules apply to their AI systems and maintain evidence that required controls are being followed. This may include documentation, risk assessments, testing records, data handling practices, security controls, and review procedures.
Keeping compliance activities connected with AI development can also make audits and internal reviews easier.
Ethical AI development begins long before a model produces its first output. Choices made during data collection, model design, testing, and deployment can all influence how an AI system behaves.
Teams should ask whether their data is appropriate, whether certain groups could be unfairly affected, and whether users can understand the system's role in important decisions.
Transparency also matters. People do not always need to understand every technical detail of a model, but they should have enough information to understand how AI is being used and when human involvement is available.
Organizations do not necessarily need to create a large governance department immediately. They can begin with a few practical steps.
First, create an inventory of AI systems and identify who owns each one. Next, classify systems according to their potential level of risk. Then establish clear rules for development, testing, approval, monitoring, and retirement.
Employee training is equally important. Governance policies have little value if developers, managers, and users do not understand their responsibilities.
Businesses should also review governance regularly. AI technology changes quickly, so policies created several years ago may not address newer models, applications, or risks.
In 2026, AI governance is becoming an important part of how organizations approach AI adoption. The focus is shifting from simply asking whether AI can perform a task to asking whether it should perform that task, under what conditions, and with what safeguards.
The strongest approach will combine technology, business processes, security, legal oversight, and human judgment. Organizations that build governance into AI development from the beginning will be better prepared to manage risks while continuing to explore new uses for the technology.
AI Governance is ultimately about creating trust around AI. When businesses know what their systems are doing, understand their risks, monitor their performance, and maintain clear accountability, they can move forward with AI in a more responsible and sustainable way.



 India

 Canada
 United Kingdom
 New Zealand
 USA
 UAE
 SGP
 Australia
 CALL
NOW